
Grok Bot, Cursor and Enterprise Agents: Choosing Where Autonomy Belongs
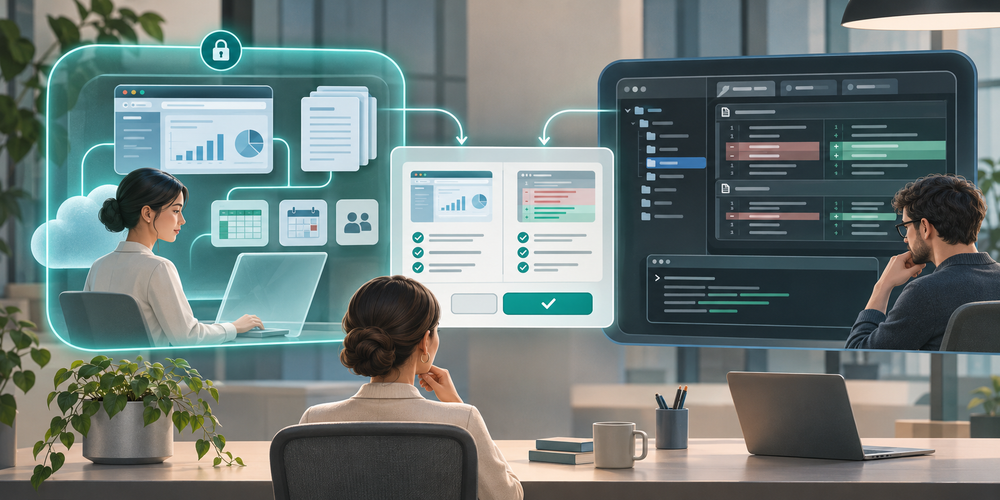
AI tools are moving from answering questions to taking actions. A coding agent can inspect a repository, edit files and run commands. A computer-use agent can move between a browser and business applications. These capabilities may look similar in a product demo, but they create different operational and security questions.
Grok Bot and Cursor illustrate the distinction. Grok Bot is presented as a cloud-based assistant that can work across apps and websites. Cursor is an AI-enabled development environment whose agent works with a codebase. One is oriented toward delegated work across applications; the other toward software engineering. Neither should be treated as a general permission to automate any task.
Two agents, two working environments
Grok Bot lets users create Bots for specific jobs and delegate tasks through chat. Its documentation describes bots working across applications, websites and tools, with integrations and custom tooling. For enterprise use, xAI describes administrative controls for access, network settings and auditing. The current security documentation also describes per-user isolation, app access granted by users or teams, and approval gates for sensitive actions. These details matter because a Bot that operates a browser or business application can interact with more than the text in a prompt. (Grok Bot overview; Grok Bot for teams and enterprises.)
Cursor’s agent is built around software development. It can search a codebase, edit multiple files, run terminal commands and show changes for review. Cursor also documents different modes and execution controls, including sandboxing and approval behaviour for certain tool calls. That makes it a distinct environment from a general-purpose Bot that uses a browser and business applications. (Cursor Agent mode; Cursor Run Modes and security controls.)
| Grok Bot | Cursor Agent | |
|---|---|---|
| Typical context | Apps, websites and connected tools for a delegated task. | A software repository and the developer tools around it. |
| Potential output | A completed multi-step task, draft or update in connected systems. | A proposed or applied code change, with related commands and checks. |
| Human review focus | What data it accessed, which actions it took and whether external changes need approval. | Whether the diff is correct, secure, tested and consistent with the project. |
| Key governance question | Which apps, accounts and actions may the Bot use? | Which files and commands may the agent access, and when does it need approval? |
This comparison is about the products’ documented design, not a claim that one is universally safer or more capable. Specific features, controls and availability can depend on the plan and change over time.
Why “can do the task” is not the right approval test
An agent may be able to complete a sequence of actions and still be a poor fit for the process. A routine browser task could involve personal information, payments or messages to customers. A seemingly small code change could affect authentication, data handling or production behaviour. The relevant question is not simply whether the tool can perform the action. It is whether the organisation can limit the scope, inspect the result, recover from an error and account for what happened.
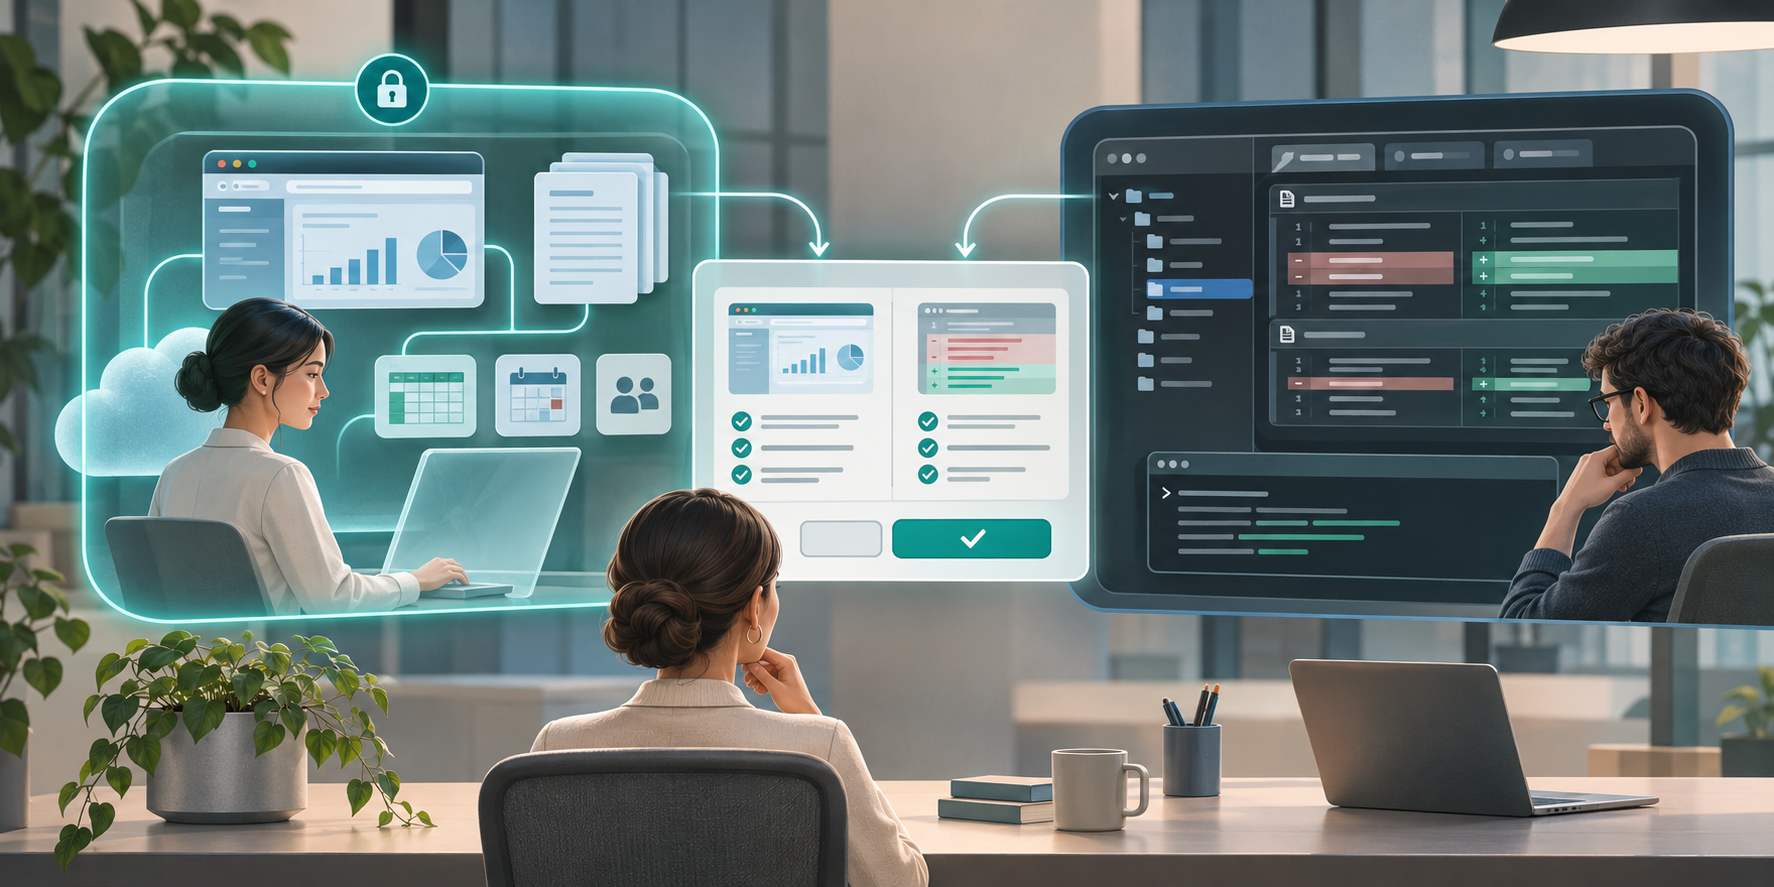
That calls for different review patterns. In an IDE, engineers can inspect a diff and run tests. In a cloud agent, reviewers may need an action log, browser recording or a clear list of connected accounts and resulting changes. A textual summary from the agent is useful, but it is not a substitute for evidence from the systems it touched.
Start with a bounded process
Choose a recurring task that is valuable but has a low cost of error. Define its boundaries before connecting a Bot or code agent:
- What is the exact input and expected output?
- Which files, websites, accounts and records are in scope?
- Which actions may the agent prepare, and which may it actually execute?
- What must always wait for a person, such as sending a message, changing a customer record or merging code?
- What evidence will the reviewer use to accept, reject or recover from the result?
Then run a supervised trial using synthetic or approved data. Keep permissions narrow, begin with read-only access when possible, and make any write action reviewable. For code, use a protected branch and the project’s normal tests. For a browser-based Bot, use a dedicated account or test environment where the workflow allows it. Record task completion, corrections, time spent reviewing and any unexpected access or actions.
Design the operating boundary before rollout
Before expanding access, decide who can create agents, connect applications, change permissions and view activity. Review whether logs are detailed enough to investigate incidents. Establish how credentials are stored and revoked, what happens when an agent encounters an unexpected page or prompt, and which actions require human confirmation. In development environments, include repository permissions, secret access, command execution and code review. In business applications, include identity, network access, records that may be read or changed and any downstream notification.
These controls are not a one-time checklist. Revisit them when the agent gains new tools, connects to another system, or moves from preparing work to executing it. A successful trial on a narrow process does not prove the agent is safe for an adjacent process with different data or consequences.
Use agents where their environment fits
Grok Bot and Cursor are not alternatives for the same job. A cloud-based Bot may fit a bounded workflow that spans approved applications. A code agent may fit a software task that needs repository context, edits and developer checks. Some organisations may use both, alongside conversational assistants and workflow automation. The architecture should follow the process, its data and the people responsible for the outcome—not the novelty of the tool.
At Emplex, we help organisations assess where AI agents can add value, define safe operating boundaries and implement suitable solutions. Contact Emplex to discuss a process you are considering.